Broad access
Saved credentials and oversized tool permissions give agents more authority than the workflow requires.
CodeCrux + AXEC / enterprise AI security
Move from an AI demo to a governed production path. CodeCrux implements AXEC so every agent action can carry identity, policy, protected access, approval, and evidence.
For security, AI, platform, and engineering teams preparing agents for real enterprise work.
The production gap
The moment an agent can read a customer record, create a task, send a message, or change a system, AI access becomes an enterprise control problem.
Identity, credentials, authorization, policy, approvals, and audit trails cannot stay disconnected from the action itself.
Saved credentials and oversized tool permissions give agents more authority than the workflow requires.
Without runtime policy, sensitive actions either run too freely or depend on scattered application logic.
When something happens, teams cannot reliably connect the user, agent, decision, provider action, and outcome.
The governed gateway
AXEC verifies identity, checks policy, enforces access in real time, and records the outcome before an agent reaches your enterprise systems.
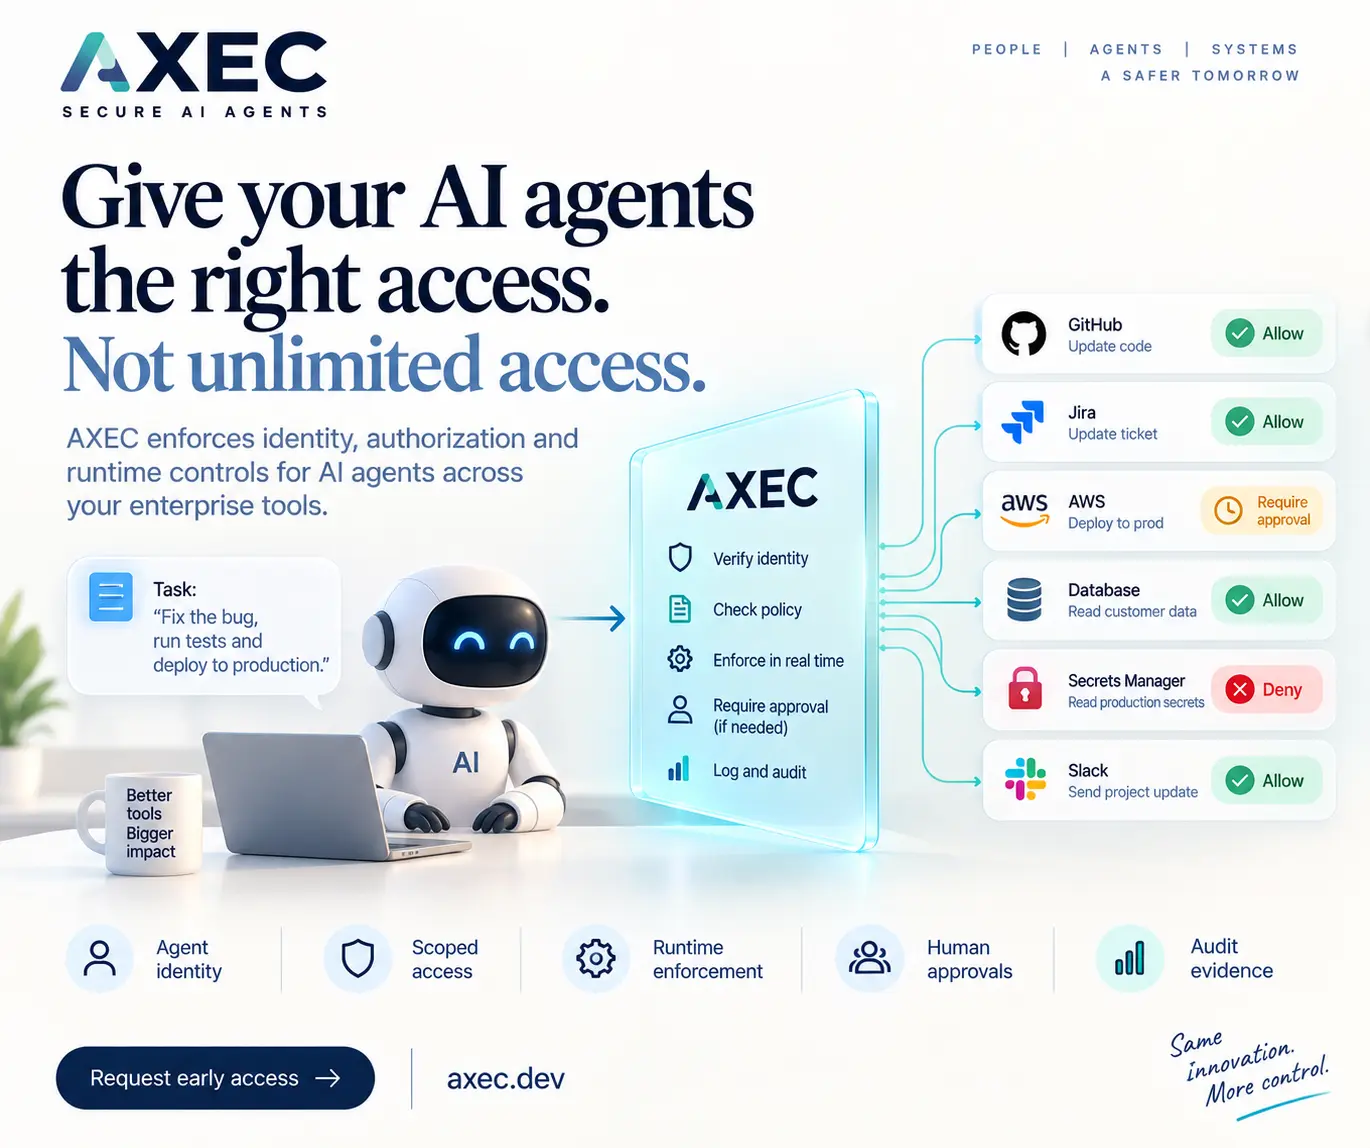
Give each agent an identity and preserve the user or service it represents through explicit delegated authority.
Govern MCP servers and API-backed capabilities through one controlled catalog with exact connector and tool ceilings.
Keep provider credentials behind the gateway and resolve the correct connection only after authority is validated.
Allow, deny, or route sensitive actions for approval using the user, agent, capability, target, and request context.
Link the authorization decision to the provider outcome while keeping secrets and bearer tokens out of evidence.
Start with one workflow
You do not need to govern every future use case on day one. Start with one valuable workflow and establish a repeatable authority path your teams can extend.
Define the business outcome, systems involved, and what must remain human-controlled.
Register the agent, connect approved systems, and preserve the requesting user context.
Set the allow, deny, and approval conditions before the agent reaches the provider.
Keep the decision, action, and provider result linked for operations and review.
First workflow idea: start with a customer-support, revenue-operations, engineering, or internal-knowledge workflow where a clear approval boundary can be measured.
Built for the buyer committee
See identity, policy decisions, approvals, credentials, and evidence in one governed path.
Keep your agent framework while adding a control layer across MCP and API-backed systems.
Start with one workflow, test its decisions, and extend the pattern as adoption grows.
Before you start
No. AXEC works with existing identity infrastructure and adds agent identity, delegated grants, connection context, and runtime authorization for actions taken on a user's behalf.
Yes. AXEC provides a consistent authorization boundary for remote MCP servers and API-backed capabilities.
Your policy decides. Routine actions can run automatically while irreversible, privileged, or consequential actions can pause for approval of that exact request.
Credentials remain behind the gateway and are selected only after an action is authorized. They are not exposed to the model or returned to the agent runtime.
Make the first workflow real
Schedule a 30-minute conversation with the AXEC team and CodeCrux. Bring one workflow, one concern, or one architecture question.
Schedule your architecture conversation